Enterprise security and compliance, across the whole platform.


SOC2 Compliant
Controls verified to operate effectively across an extended audit period.
HIPAA Compliant
BAAs executed with every subprocessor that touches PHI. Customer BAAs on request.
GDPR Compliant
Lawful basis, data-subject rights, and processing controls in place. DPA available.
Every control, mapped from our SOC 2 audit. Grouped to match how your review is structured.
Security control 1
01 / 05

Scroll to advance through each control
01 / 05
Access Control

Role-Based Access Control across all layers
MFA required for staff on production
Least-privilege access, reviewed on role change
All access events logged and auditable
Vendor access bound by DPAs
Periodic access reviews
02 / 05
Data Security
TLS 1.2 or higher enforced in transit
AES-256 at rest, including recordings & transcripts
Configurable retention with automated deletion
Logical multi-tenant isolation
No card data stored (Stripe tokenization)
Data classified by sensitivity
03 / 05
Infrastructure and Network
Google Cloud Platform, US data centers
Private VPC isolation
Anti-DDoS and network firewall rules
Separate production, staging, and development
Multi-zone redundancy and failover
Hardened images, automated patching
04 / 05
Application & Product Security
Web Application Firewall on all public endpoints
Dependency and vulnerability scanning
Secrets managed in GCP Secret Manager
SSO with account-level MFA enforcement
Full audit logs in the dashboard
Configurable AI disclosure controls
05 / 05
Availability and Reliability
99.9% uptime SLA
Automated multi-zone failover
24/7 monitoring with alerting
Documented incident response plan
Every subprocessor, and exactly what each one processes. Published and maintained in real time. You are notified of any change.
How data moves through SquawkVoice
From intake to deletion, across every channel.
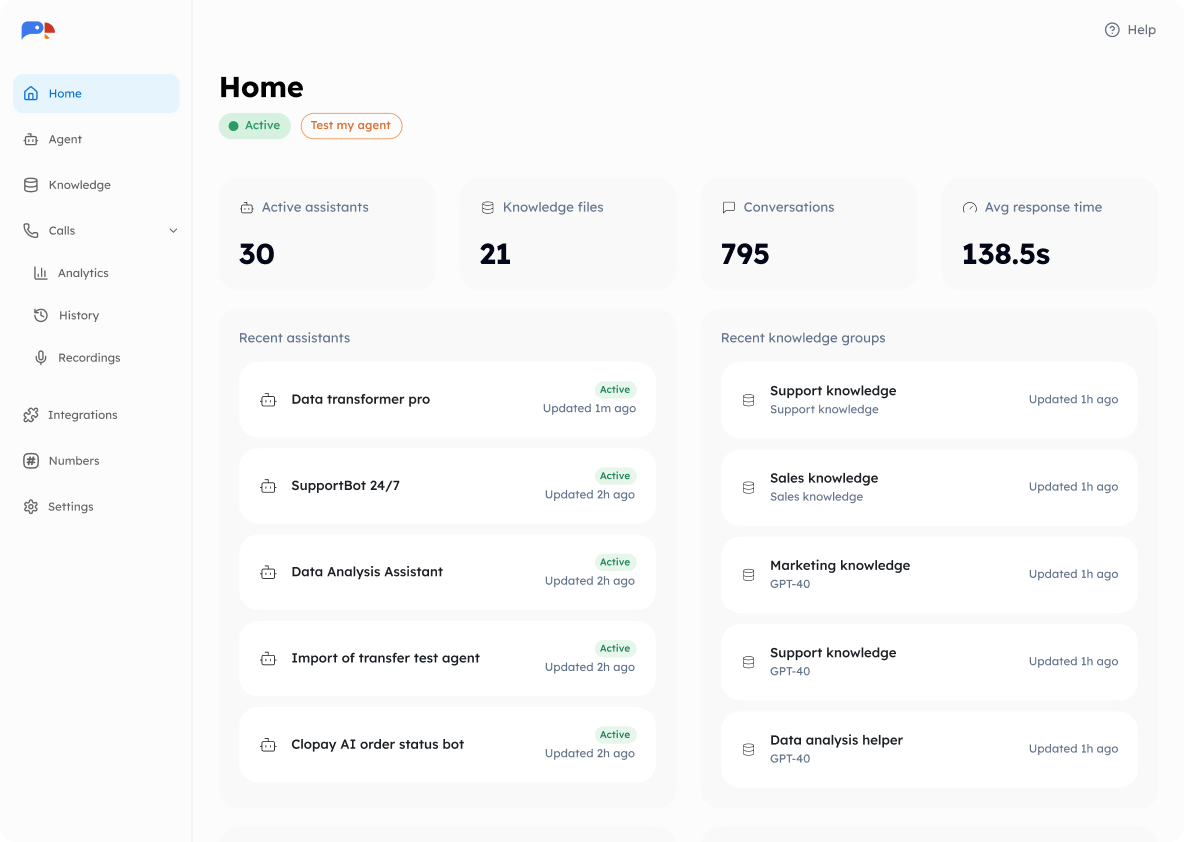
Your data belongs to you.
Retention
Isolation
Financial data
Audit trails
Every incident response has a process
Detection
Containment
Notification
Remediation
Everything your security and procurement teams need, in one place.
SOC2 Compliant report.
Full independently audited report available under NDA for your review file. Request via security@squawkvoice.ai.
Questionnaires
We complete VSA, SIG, CAIQ, and custom security questionnaires.
DPA and BAA
Data Processing Addenda and Business Associate Agreements on request.
Responsible disclosure is acknowledged within 2 business days, with a remediation timeline within 10. Contact security@squawkvoice.ai.
See SquawkVoice in action.
Get a walkthrough of the platform, or have our team answer your security questions directly.